Tracing a hacked WordPress site's malware to a single database trigger, and rebuilding it clean
Business typeSmall business website
PlatformWordPress
Services usedMalware removal, indexation recovery, site rebuild
Thousandsof spam pages traced to a single malicious database trigger
Root causefound and removed, not just the visible symptoms
Verified cleanbefore the site was handed back
The challenge
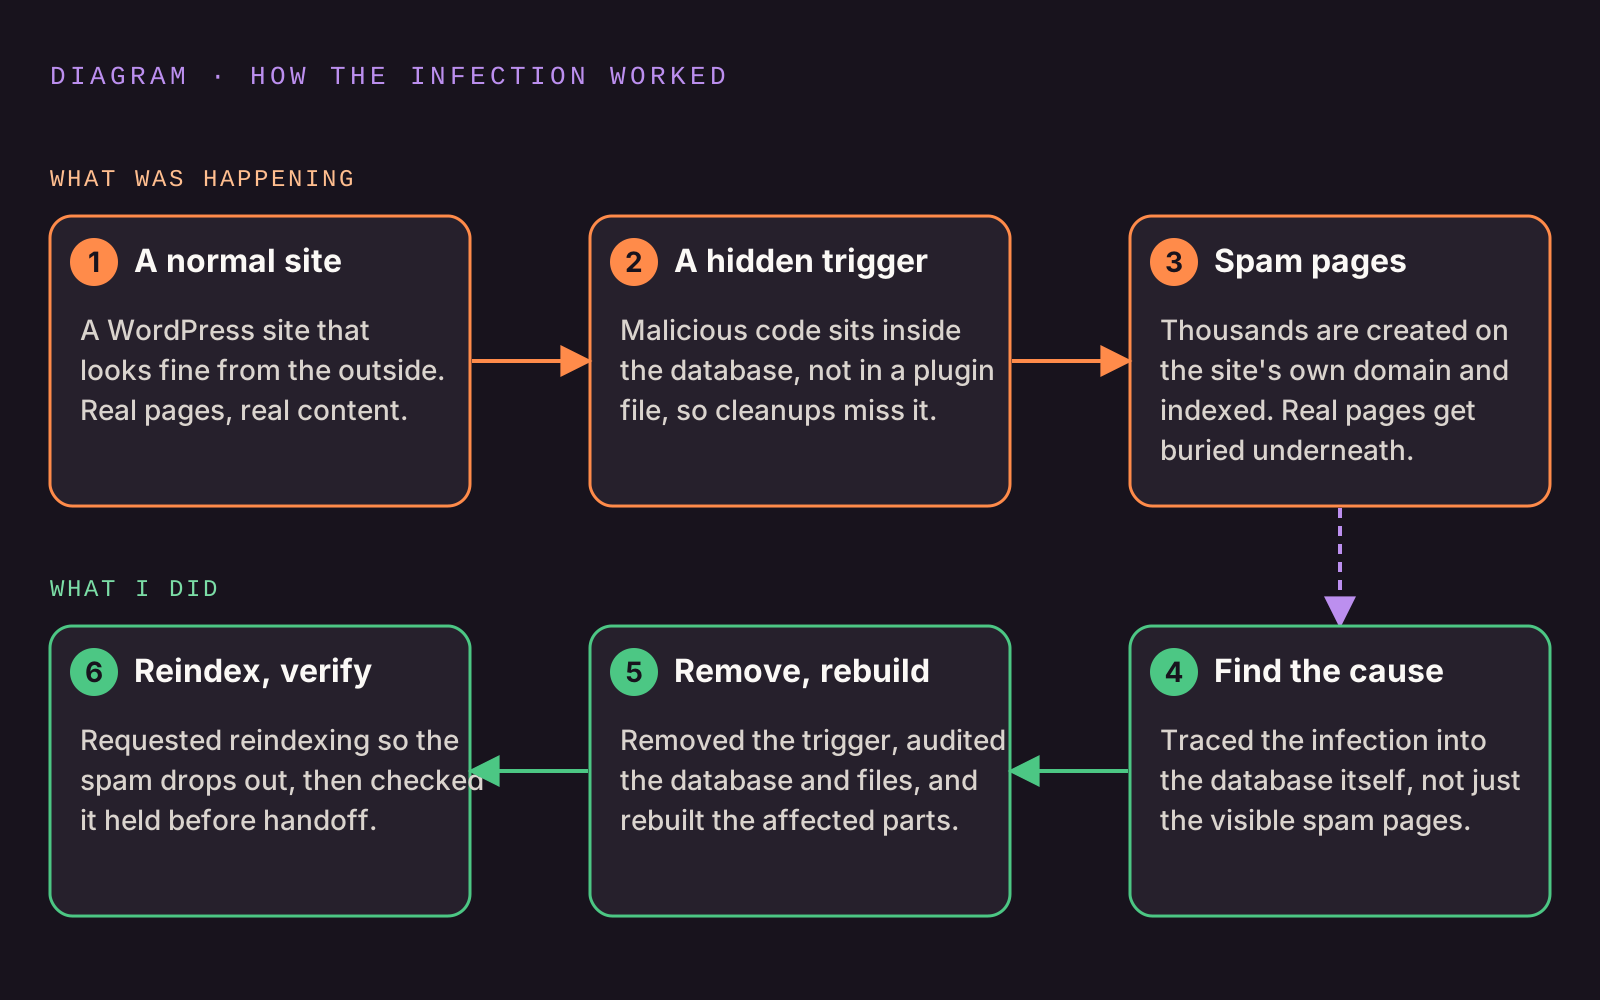
A WordPress site was quietly compromised through a malicious database trigger: infected code sitting inside the database rather than in a plugin file, which is why it kept surviving normal cleanup attempts. It was silently generating thousands of spam pages.
Google was indexing those pages. The site's real content was getting buried under junk, putting its entire search presence at risk.
A malicious trigger embedded directly in the database, not in a theme or plugin file, which is why earlier cleanups hadn't held
Thousands of auto-generated spam pages being created and indexed under the site's own domain
No clean, verified backup to restore from, so the fix had to happen in the live database
What I did
Traced the infection to its root cause inside the database rather than just deleting the spam pages
Removed the malicious trigger and audited the rest of the database and file system
Rebuilt the affected parts of the site clean and requested reindexing through Search Console
Verified the fix held over time before handing the site back
The outcome
The malicious trigger was fully removed, not just its symptoms, and the rebuild was verified clean before handoff.
The spam pages dropped out of Google's index over the following weeks, and the site's real pages returned to their earlier search visibility.
The process
How the infection worked and what I did about it. An illustration of the process, not real data.